Tech
Chase, Wells Fargo and Other Big US Banks Hit by Online Outages
Chase says a software bug slowed transactions at big US banks on Monday, with customers reporting problems at Chase, Wells Fargo and Bank of America.
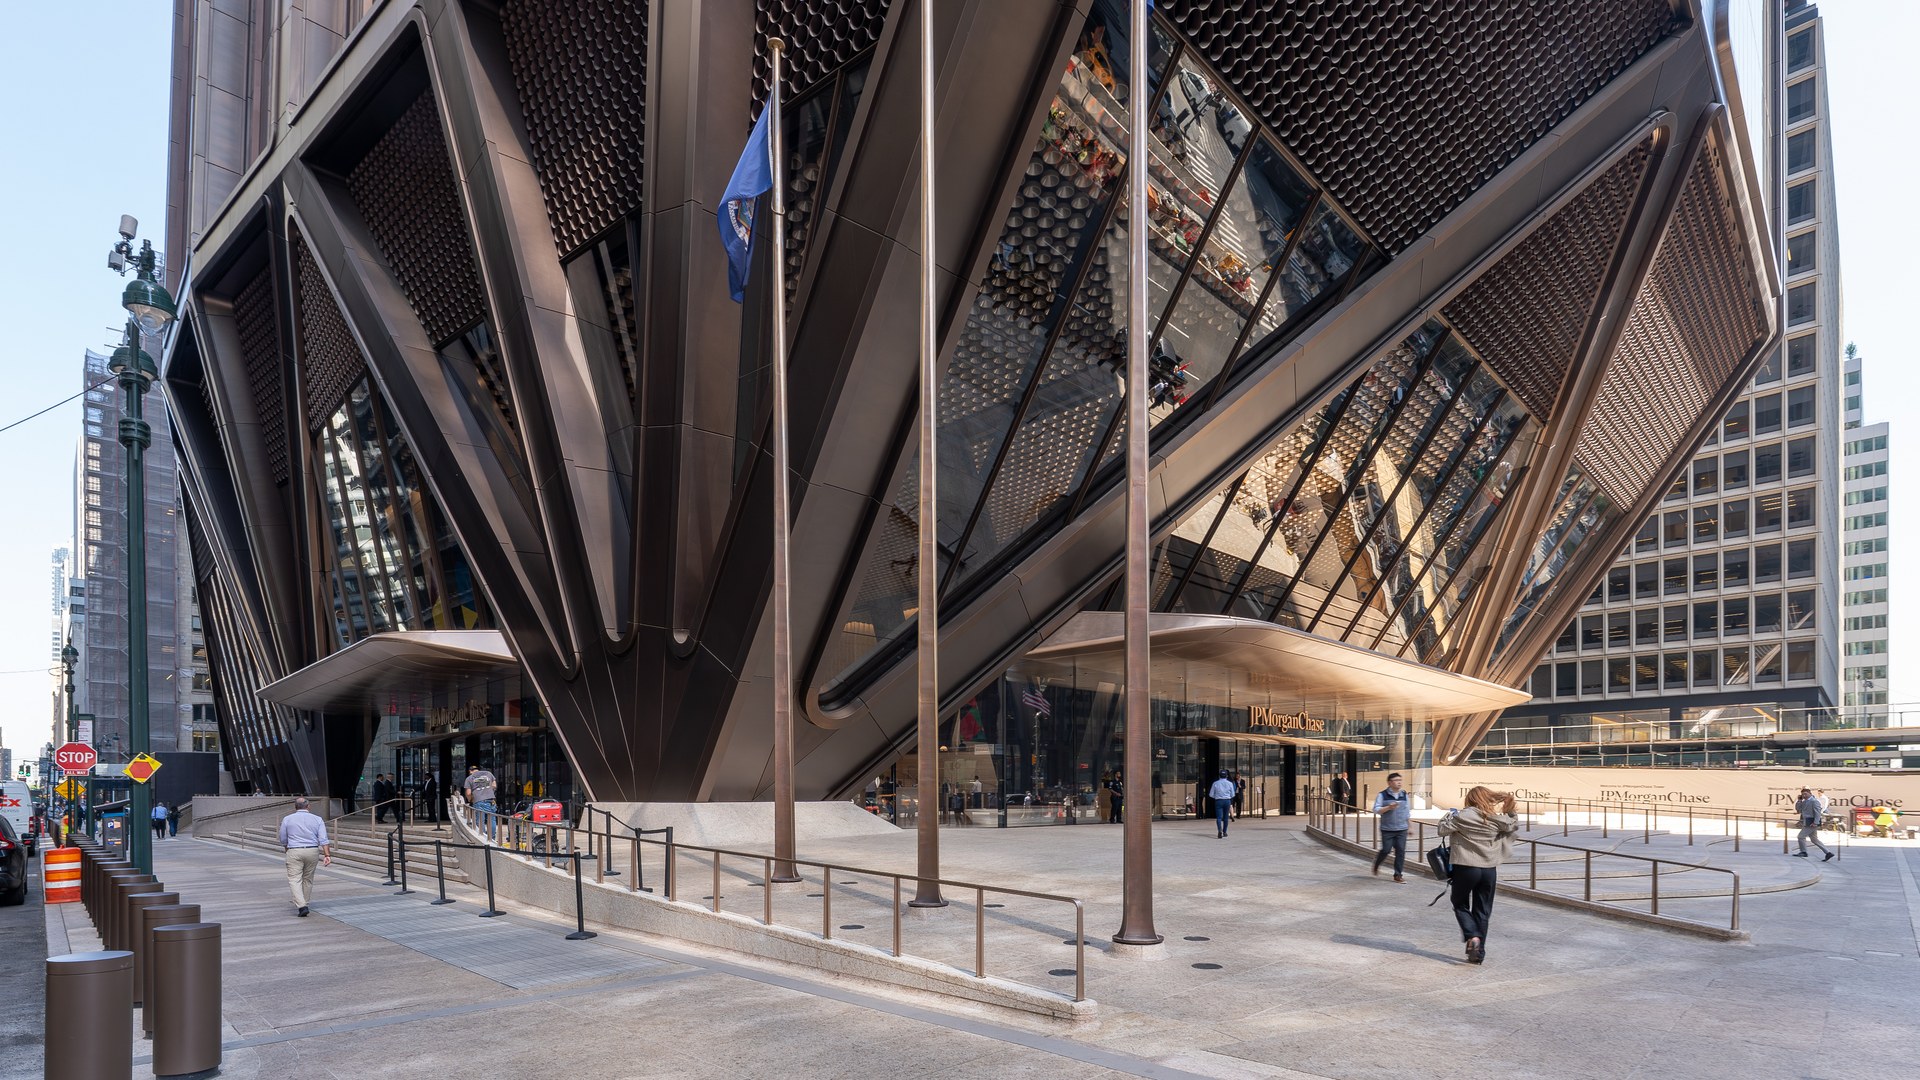
TL;DR — the direct answer: JPMorgan Chase, Visa and Mastercard said on Thursday, 19 November, that third-party vendors serving them were hit in a cyberattack, exposing customer marketing data including names and email addresses. All three stressed that their own systems and payment networks were not affected, and that no payment data, such as card numbers, was taken. The disclosures followed claims by an extortion group calling itself n0n, which emerged in September and posted files on 16 November said to come from suppliers serving the three companies. Reuters reviewed posted material appearing to contain more than 16,000 JPMorgan customer email addresses and 124 bank employee addresses, some with phone numbers and postal codes, but could not verify its authenticity. No company has named the vendor or vendors involved. JPMorgan said the attack is unrelated to a separate software-bug outage that disrupted some customers earlier in the week.
What happened: The three disclosures landed within a day of each other, and each company described the exposure as limited to marketing or contact data. JPMorgan said third parties that provide services to the firm were the target of a cyberattack, and that attackers accessed certain marketing data held by those vendors, which may include some customer names and email addresses. The bank said there is no disruption to its services, that it will contact affected customers directly, and that it will offer support including credit monitoring. Visa said the claims are associated with an incident involving a third-party service provider in Asia Pacific, that Visa's systems were not involved and were not impacted, and that no payments data such as card numbers was affected. Mastercard said a third-party provider exposed a limited amount of email addresses, non-payments information, from a small subset of cardholders enrolled in a specific benefit program, that there is no impact to the payment network or to people's ability to use their cards, and that the exposure has been contained. The timeline began earlier in the month: on 11 November, n0n claimed an intrusion at Qubole, a cloud data platform, and on 16 November it posted files it said came from suppliers serving the three companies. The group has claimed roughly 200 incidents since emerging in September, according to eCrime.ch.
Why it's trending: Three of the biggest names in global payments disclosing cyber incidents on the same day is a story in itself, and the timing made it bigger. The disclosures came at the end of a week of technology failures across the United States: a Federal Aviation Administration outage that triggered a nearly five-hour nationwide ground stop, outages that froze accounts at major banks including Chase, disruption at United Airlines and across Microsoft's services, and an outage on the National Security Agency's internal network. The same day, the White House replaced its national cyber director, Sean Cairncross, with the Pentagon's chief information officer, Kirsten Davies. The incident also puts the spotlight on third-party risk, the weak link in modern finance: the banks and card networks were not themselves breached, but outside firms holding their customers' marketing data were, and none of the three companies has said which firms those were. For customers, the practical question is immediate and personal: names and email addresses are exactly the raw material for phishing emails that impersonate a bank or a card provider, and the data posted online reportedly includes phone numbers and postal codes as well.
Background / context: The distinction the companies are drawing matters. Payment data means card numbers, account credentials and the systems that move money, and all three companies say none of that was touched. Marketing data means the contact and campaign information that outside firms hold on a bank's behalf: names, email addresses, and in the posted material, some phone numbers and postal codes. That data cannot by itself drain an account, but it can make a scam email look convincing, because it lets a fraudster address a victim by name and pretend to be their bank. JPMorgan is the largest bank in the United States, and the incident is separate from the outage some of its customers saw earlier in the week, which the bank attributed to a software bug affecting transaction processing, not to an attack. Our earlier report on that outage covered Chase and Wells Fargo customers finding their online banking frozen. Security firms have documented stolen Qubole credentials being used to reach customer environments through trusted integration access. But the link between Qubole and these three incidents has not been confirmed by any of the companies, and it should not be treated as established.
What we know / what's unconfirmed: Confirmed: the three disclosures on Thursday, 19 November; JPMorgan's statement that attackers accessed marketing data held by its vendors, possibly including customer names and email addresses; Visa's statement that its incident involved a third-party provider in Asia Pacific and that no card numbers were affected; Mastercard's statement that a limited number of email addresses from a small subset of cardholders in one benefit program were exposed and the exposure is contained; that n0n posted claims and files on 16 November after claiming a Qubole intrusion on 11 November; that the group has claimed roughly 200 incidents since September, according to eCrime.ch; and that JPMorgan says the attack is unrelated to the earlier software-bug outage. Two things need flagging. First, the figures in the posted data are claims, not confirmed facts: Reuters reviewed material appearing to contain more than 16,000 JPMorgan customer email addresses and 124 employee addresses, and described Visa data focused on Asia Pacific markets including Hong Kong, Taiwan, Korea, Japan, the Philippines, Singapore, Malaysia, Australia and Macau, and Mastercard data covering North America, the Middle East and Africa, but Reuters could not independently verify the authenticity of any of it. Second, no company has named the vendor or vendors involved, and The Register reports that none of the three identified the affected providers, the precise timing of the incidents or the full details of what was taken. Unconfirmed: whether the three incidents share a single vendor, whether Qubole is involved at all, how many customers are affected in total, and how the attackers got in.
What happens next: JPMorgan says it will contact affected customers directly and offer support, including credit monitoring, so customers who hear from the bank should check that any message genuinely comes from it before clicking anything. The three companies say their investigations continue. The practical risk for customers is phishing: with names, email addresses and phone numbers in circulation, fake emails and calls impersonating Chase, Visa or Mastercard are likely, and customers should be wary of any message asking them to update payment details or share a one-time code. Regulators and lawmakers are likely to ask why three of the largest financial firms were exposed through the same kind of outside supplier at the same time. The incident also lands in a wider debate about third-party risk: the systems that move money held up, but the firms around them did not.
Q: What happened to JPMorgan, Visa and Mastercard?
A: All three said on Thursday, 19 November, that third-party vendors serving them were hit in a cyberattack. JPMorgan said attackers accessed marketing data held by its vendors, possibly including customer names and email addresses. Visa linked its incident to a third-party provider in Asia Pacific, and Mastercard said a limited number of email addresses from a small subset of cardholders in one benefit program were exposed.
Q: Was my card number or money affected?
A: According to all three companies, no. They say their own systems and payment networks were not affected, and no payment data such as card numbers was taken. What was exposed is marketing and contact information: names, email addresses, and in the posted material, some phone numbers and postal codes.
Q: Who is behind the attack?
A: An extortion group calling itself n0n, which emerged in September 2026 and has claimed roughly 200 incidents since then, according to the cybercrime research platform eCrime.ch. The group claimed an intrusion at the cloud data platform Qubole on 11 November and posted files on 16 November. The Qubole link is unconfirmed, and the posted data has not been verified.
Q: Which vendor was breached?
A: None of the three companies has named the vendor or vendors involved. Visa said only that its incident involved a third-party service provider in Asia Pacific. It is not confirmed whether the three incidents share a single vendor, or whether Qubole, named in online claims, is involved at all.
Q: What should customers do?
A: Be wary of emails, calls or messages claiming to be from Chase, Visa or Mastercard and asking you to update payment details or share a one-time code, since the exposed names and email addresses can make phishing attempts look convincing. JPMorgan says it will contact affected customers directly and offer support including credit monitoring. Do not click links in unexpected messages; contact your bank through its known channels instead.
Sources: Channel News Asia — JPMorgan, Visa, Mastercard say third-party vendors targeted in cyberattack, Moneycontrol — Visa, Mastercard, JPMorgan disclose customer data exposure in third-party vendor cyberattack, Economic Times CISO — JPMorgan, Visa, and Mastercard Face Cyber Incidents: Customer Data Leaked, and The Statesman — JPMorgan, Visa, Mastercard data breach: What was exposed in third-party cyberattacks?.
Chase says a software bug slowed transactions at big US banks on Monday, with customers reporting problems at Chase, Wells Fargo and Bank of America.
Microsoft says Microsoft 365 is fully restored after a 38-hour outage hit Outlook, Teams and Copilot in 70-plus countries, and rules out a cyberattack.
United Airlines resolved a systemwide outage that delayed departures on Monday, days after the FAA ground stop snarled US air travel.