LIVE
Russia and Ukraine Agree Their Biggest Prisoner Swap of the War  •  House Blocks the Hegseth Impeachment 211-204  •  OpenAI Tops $10 Billion in a Single Quarter
Tech

DeepMind's AI Just Proved Signal's Encryption With Maths — Down to the Machine Code

Trending Now • 12 November 2026 • 4 min read

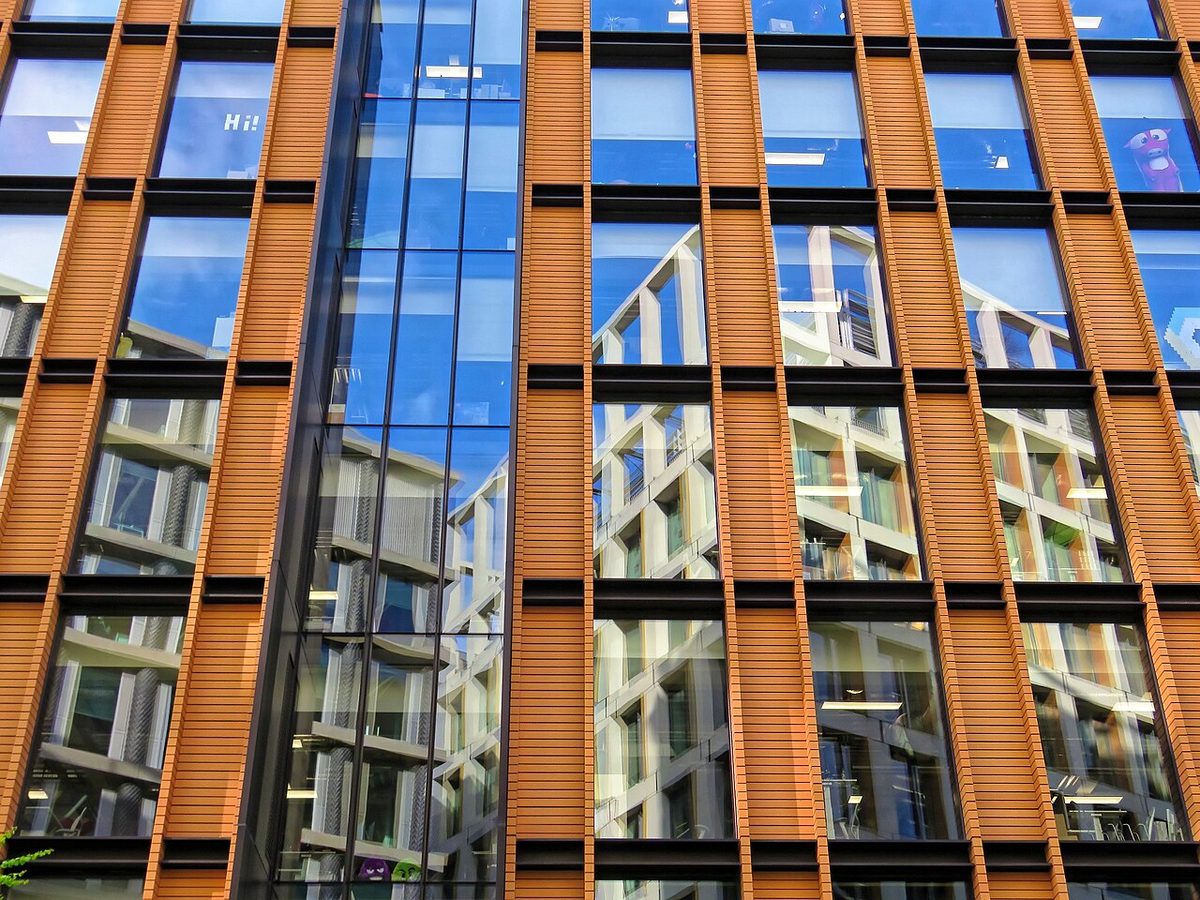
The glass facade of 6 Pancras Square, Google's London headquarters at King's Cross, home to Google DeepMind

Photo: Acabashi, CC BY-SA 4.0, via Wikimedia Commons — Google's headquarters at 6 Pancras Square, King's Cross, London, home to Google DeepMind.

TL;DR — the direct answer: Google DeepMind has used AI to do something long considered a grand challenge in software security: mathematically prove that the actual code behind Signal's encryption does what it promises — down to the compiled machine code running on real phones. The work, published on 10 November, is the first time a widely deployed cryptographic protocol has been formally verified at this depth, by any method.

What happened: DeepMind announced AlphaProof Code on Monday, 10 November — an agentic framework for formal verification that combines human expertise with AI agents. A team of five researchers spent four weeks with it, guiding AI agents to formally verify the code of Signal's cryptographic protocol, the technology that protects billions of private conversations in apps like Signal and Google Messages. The agents, powered by Gemini, generated over six million lines of Lean — a computer language that mathematically proves the accuracy of code — and every proof was checked by Lean's kernel. DeepMind says the work marks the first time AI has been used to formally verify a widely deployed cryptographic protocol at this depth.

Why it's trending: Most protocol verification stops at the design level: researchers prove the maths of the protocol on paper, and trust that the code implements it correctly. DeepMind's agents went further, proving properties of the compiled code itself — the exact instructions running on ARM devices. The work covers the two things that matter most in a messenger: the PQXDH handshake that sets up a conversation, and the Triple Ratchet that rotates the key for every message. The team proved four properties of that code: messages stay secret, the other side is who they claim to be, past messages stay secret even if a key leaks later, and the conversation recovers its security after a compromise. A task that would historically take expert teams years took four weeks.

Background / context: The target was libsignal version 0.105.4, the reference implementation of the Signal protocol, compiled for ARM Linux inside a test harness. To confirm the system can tell correct code from buggy code, the team reintroduced two real, previously fixed bugs into an isolated version of Signal's code. In both cases, AlphaProof Code produced a machine-checked proof that the buggy version was insecure. The full set of verification artifacts has been open-sourced, so other researchers can inspect and reproduce the proofs. The work sits inside a bigger shift: AI agents are moving from writing code to proving code correct, and DeepMind is positioning AlphaProof Code as a tool for the most security-critical software — the kind where a bug can compromise billions of users at once.

What we know / what's unconfirmed: Confirmed: the announcement, the four-week timeline, the six-million-plus lines of Lean proof, the scope — one-to-one sessions using the PQXDH handshake and Triple Ratchet, compiled to AArch64 machine code — and the two-bug validation test. Also confirmed: the limits. The proof covers one-to-one sessions only; group messaging is listed as future work. It applies to libsignal 0.105.4 in a test harness, not to the full Signal app on your phone — the app, the servers, the key servers and the safety-number UI are not covered. The cryptographic primitives themselves are modelled as assumptions, not proved. So this is not a certificate that Signal is unhackable, and no user needs to change anything: there is no emergency patch or account change tied to the announcement.

What happens next: DeepMind says the framework can be applied to other security-critical code, and the open-sourced artifacts invite the research community to test the claims. The immediate question is scope: group chats, linked devices and other architectures are the obvious next targets. The bigger question is whether formal verification — long too slow and expensive for most software — becomes practical now that AI agents can do the heavy lifting. If it does, the way the most sensitive code in the world gets checked may have just changed.

Frequently asked questions

Q: What did DeepMind actually prove?
A: That the compiled code of Signal's cryptographic protocol — the PQXDH handshake and Triple Ratchet in libsignal — delivers four security properties: secrecy, authentication, forward secrecy and post-compromise security, down to ARM machine code.

Q: Does this mean Signal is unhackable?
A: No. The proof covers one-to-one sessions in libsignal 0.105.4, not the full app, servers, group chats or linked devices, and the cryptographic primitives are assumed correct rather than proved.

Q: How long did the verification take?
A: Four weeks, with a team of five researchers guiding AI agents powered by Gemini, which generated over six million lines of machine-checked Lean proof.

Q: How did they test the system?
A: They reintroduced two real, previously fixed bugs into an isolated copy of Signal's code. In both cases AlphaProof Code produced a machine-checked proof that the buggy version was insecure.

Q: Do Signal users need to do anything?
A: No. There is no emergency patch or account change tied to the announcement, and the result does not replace app updates or safety-number verification.

Sources: Google DeepMind — Formal Verification of Signal's Protocol with Gemini, Dev.to — AI Just Proved Signal's Encryption With Math. Here's What That Actually Means, and ReaderSpice — AlphaProof Code Verifies Signal Security: Scope and Limits.

← Back home